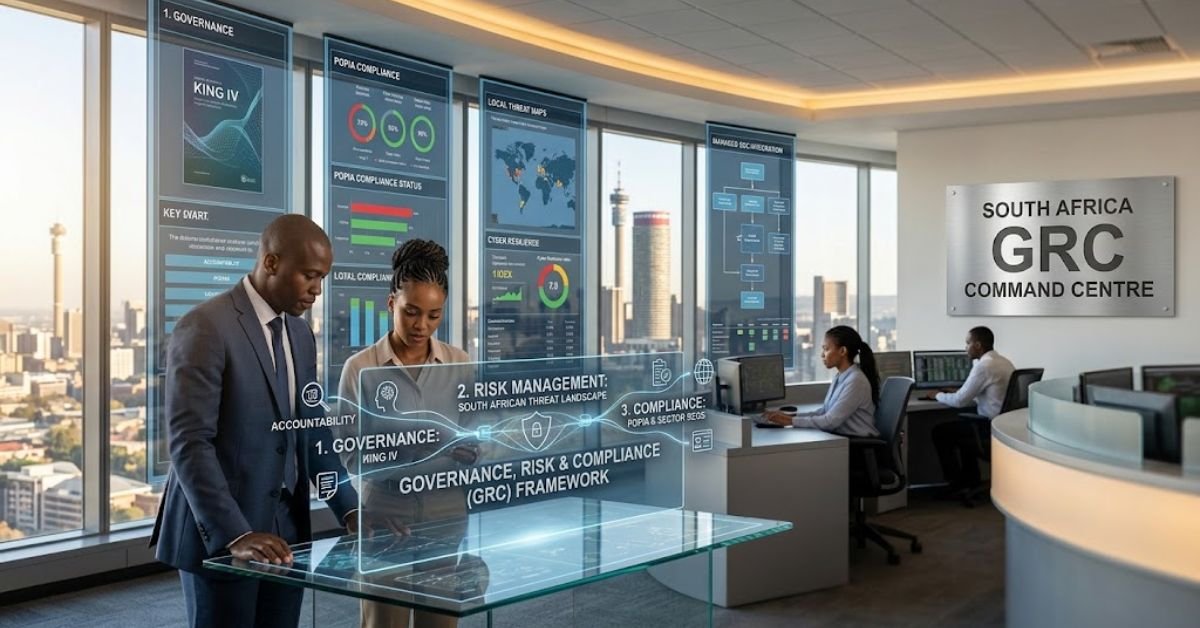
South African organisations are operating in one of the most complex regulatory and threat landscapes on the continent. Between the Protection of Personal Information Act (POPIA), King IV governance principles, sector-specific regulations, and an ever-expanding menu of cyber threats, businesses can no longer treat governance, risk, and compliance (GRC) as a once-a-year checkbox exercise. It …