South African organisations are operating in one of the most complex regulatory and threat landscapes on the continent. Between the Protection of Personal Information Act (POPIA), King IV governance principles, sector-specific regulations, and an ever-expanding menu of cyber threats, businesses can no longer treat governance, risk, and compliance (GRC) as a once-a-year checkbox exercise. It has become a continuous discipline that touches every department, from IT and finance to human resources and the boardroom.
Many companies still approach GRC reactively, scrambling to patch gaps only after an audit finding or a security incident forces their hand. This approach is costly, stressful, and ultimately ineffective. A more sustainable path is to build GRC into the operational fabric of the business from the outset. Organisations that want a structured, professionally guided approach to this work often turn to specialists such as Prima Secure, Governance risk compliance, who help translate abstract regulatory requirements into practical, day-to-day controls that actually reduce risk rather than simply satisfying a checklist.
What Governance, Risk, and Compliance Actually Means
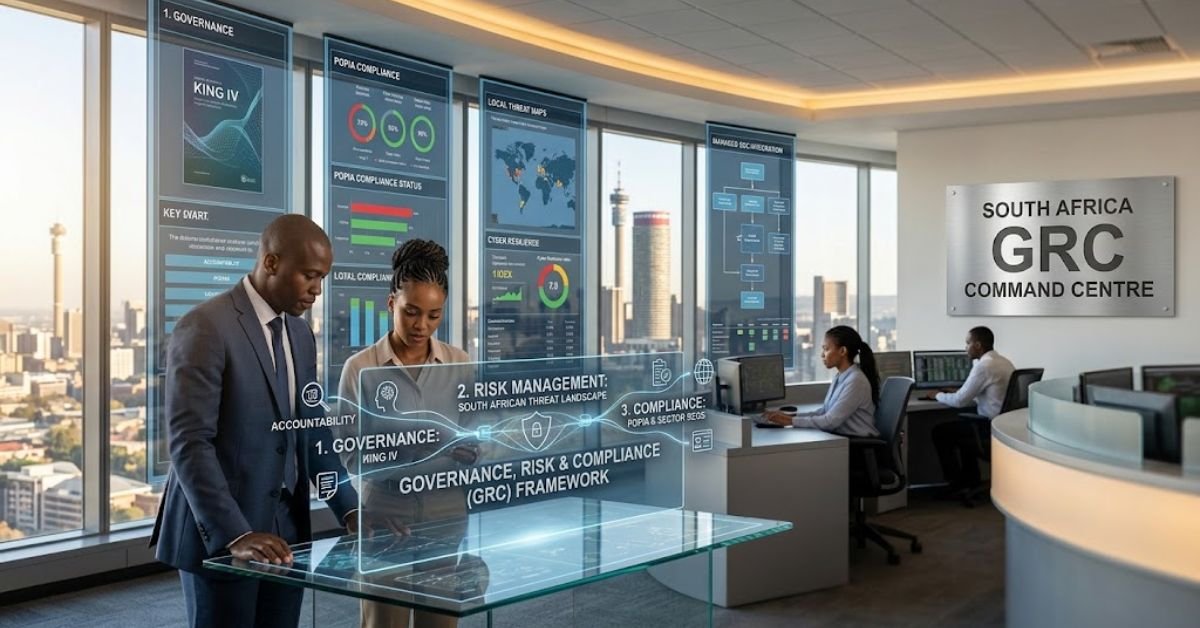
GRC is often used as a single acronym, but it represents three distinct, interconnected functions:
Governance refers to the structures, policies, and decision-making processes that ensure an organisation is run responsibly and in line with its stated objectives. This includes clear accountability at board and executive level, documented policies, and oversight mechanisms that make sure decisions are made transparently and consistently.
Risk management is the systematic process of identifying, assessing, and mitigating threats to the organisation whether those threats are cyber-related, operational, financial, or reputational. Effective risk management doesn’t try to eliminate all risk; it aims to understand risk well enough to make informed decisions about which risks to accept, transfer, mitigate, or avoid.
Compliance is the ongoing effort to meet legal, regulatory, and contractual obligations. In South Africa, this typically includes POPIA, the Cybercrimes Act, industry-specific requirements (such as those from the Financial Sector Conduct Authority for financial services firms), and increasingly, international standards like ISO 27001 or the NIST Cybersecurity Framework for companies doing business internationally.
When these three functions work together rather than in isolated silos, an organisation gains a much clearer picture of where it stands and what it needs to do next.
Why South African Businesses Can’t Afford to Ignore GRC
There are several forces converging that make GRC a business-critical function rather than a nice-to-have.
Regulatory Pressure Is Increasing
POPIA enforcement has matured significantly since the Information Regulator became fully operational. Companies that fail to demonstrate reasonable technical and organisational measures to protect personal information face real financial and reputational consequences. Beyond POPIA, sector regulators are tightening their own cybersecurity and data protection expectations, meaning many businesses now have to satisfy multiple overlapping frameworks simultaneously.
Cyber Threats Are More Sophisticated and More Frequent
South African organisations have increasingly become targets for ransomware, business email compromise, and supply chain attacks. Attackers don’t discriminate by company size; small and mid-sized businesses are often seen as easier targets precisely because they tend to have weaker governance structures and fewer dedicated security resources. Without a risk-based approach to identifying where the organisation is most exposed, businesses end up spending money on the wrong controls while leaving genuine vulnerabilities unaddressed.
Customers and Partners Expect It
Increasingly, procurement processes especially with larger corporates, government entities, and international partners require proof of a functioning GRC programme before a contract is even considered. Vendor risk assessments, security questionnaires, and requests for compliance certificates have become standard practice. Businesses without documented governance and risk processes can find themselves excluded from lucrative opportunities simply because they can’t demonstrate maturity.
Insurance and Liability Considerations
Cyber insurance providers are asking harder questions before issuing or renewing policies. Demonstrable risk management practices documented incident response plans, access controls, regular risk assessments can directly affect the availability and cost of cover. In the event of an incident, having a clear GRC trail can also make the difference in liability disputes and regulatory investigations.
See Also: Codes Error RCSDASSK: Full Fix Guide (Win, Mac, Linux)
Building a Practical GRC Framework: Where to Start
For businesses that haven’t yet formalised their GRC approach, the process can feel overwhelming. Breaking it down into manageable stages helps.
1. Establish Governance Foundations
Start with clear ownership. Who is accountable for risk and compliance at an executive level? Even smaller organisations benefit from designating a specific person or small committee responsible for overseeing governance activities, rather than leaving it as an unassigned responsibility that quietly falls through the cracks.
Document your core policies: acceptable use, data protection, incident response, access control, and third-party risk. These don’t need to be lengthy legal documents, they need to be clear, actionable, and actually followed by staff.
2. Conduct a Risk Assessment
You cannot manage what you haven’t identified. A structured risk assessment should map out:
- Critical assets and data (what needs the most protection)
- Potential threats to those assets (cyber, physical, operational)
- Existing controls and their effectiveness
- Gaps that represent unacceptable exposure
This exercise shouldn’t be a once-off event. Threats evolve, technology changes, and business operations shift risk assessments need to be revisited at regular intervals, ideally annually or after any significant change to systems or processes.
3. Map Compliance Obligations
List every regulatory, contractual, and industry requirement your organisation is subject to. For most South African businesses, this will include POPIA at minimum, but may extend to industry-specific requirements or international standards if you work with overseas clients. Understanding exactly what applies to your business prevents both under-compliance (leaving you exposed) and over-compliance (wasting resources on requirements that don’t apply to you).
4. Implement and Monitor Controls
Once gaps are identified, prioritise remediation based on risk severity rather than trying to fix everything simultaneously. Technical controls, firewalls, endpoint protection, multi-factor authentication, encryption should be paired with administrative controls like staff training and regular policy reviews.
Monitoring is where many GRC programmes fall short. Controls that aren’t actively reviewed tend to degrade over time as systems change and staff turnover introduces new gaps. Continuous monitoring, whether through internal audits or managed services, keeps the framework relevant rather than becoming a static document that gathers dust.
The Role of Frameworks Like NIST
Many South African organisations look to the NIST Cybersecurity Framework as a practical structure for organising their security efforts, even though it originates from the United States. NIST’s five core functions Identify, Protect, Detect, Respond, and Recover provide a logical, widely recognised way to structure a security programme that maps naturally onto broader GRC objectives.
Using a recognised framework like NIST also has a secondary benefit: it gives businesses a common language when communicating with auditors, insurers, clients, and regulators. Rather than describing security measures in ad hoc terms, organisations can point to a structured, internationally understood approach that demonstrates maturity and intent.
Managed Security Services and GRC: A Natural Pairing
For many small and mid-sized businesses, building an in-house GRC function from scratch is neither practical nor cost-effective. This is where managed security services, particularly managed Security Operations Centre (SOC) capabilities, play a valuable role.
A managed SOC provides continuous monitoring of an organisation’s network and systems, detecting anomalies and potential threats in real time. This operational visibility feeds directly into the risk management side of GRC you can’t accurately assess risk without understanding what’s actually happening across your environment. Threat detection data, incident logs, and response times all become evidence that supports compliance reporting and governance reviews.
Combining managed SOC services with structured GRC advisory work means businesses get both the operational monitoring and the strategic oversight needed to keep the whole system functioning coherently, rather than treating security tooling and compliance documentation as separate, disconnected efforts.
See Also: How to Use Right Networks File Manager (+ Fast Fixes)
Common Mistakes to Avoid
Treating compliance as the end goal. Being compliant with a regulation doesn’t automatically mean you’re secure. Compliance sets a minimum bar; genuine risk management often requires going further.
Copy-pasting policy templates. Generic policies downloaded from the internet rarely reflect how your organisation actually operates. Staff quickly recognise policies that don’t match reality, which undermines the credibility of the entire programme.
Ignoring third-party risk. Vendors, contractors, and partners with access to your systems or data represent an extension of your risk surface. A GRC programme that only looks inward misses a significant category of exposure.
Under-resourcing ongoing review. GRC is not a project with a defined end date it’s an operational capability that needs sustained attention, budget, and executive support.
Building Long-Term Resilience
Organisations that invest properly in governance, risk, and compliance tend to weather incidents better, recover faster, and maintain stronger relationships with regulators, clients, and insurers. The upfront effort of establishing clear policies, conducting honest risk assessments, and mapping compliance obligations pays dividends when an incident does occur and in South Africa’s current threat environment, it’s a question of when, not if.
Whether you’re building a GRC function from the ground up or refining an existing one, the goal remains the same: create a business that understands its risks, meets its obligations, and can demonstrate that understanding clearly to anyone who asks. That clarity isn’t just good practice, it’s increasingly a competitive advantage in a market where trust and demonstrable security maturity matter more than ever.
